BLOG DETAILS
Sachin Pathak

IaC

09 October, 2025
Infrastructure as Code: Terraform Best Practices
Infrastructure as Code only pays off if it stays clean. After provisioning a lot of AWS and Azure with Terraform, here are the practices that keep it maintainable.
Remote state and locking
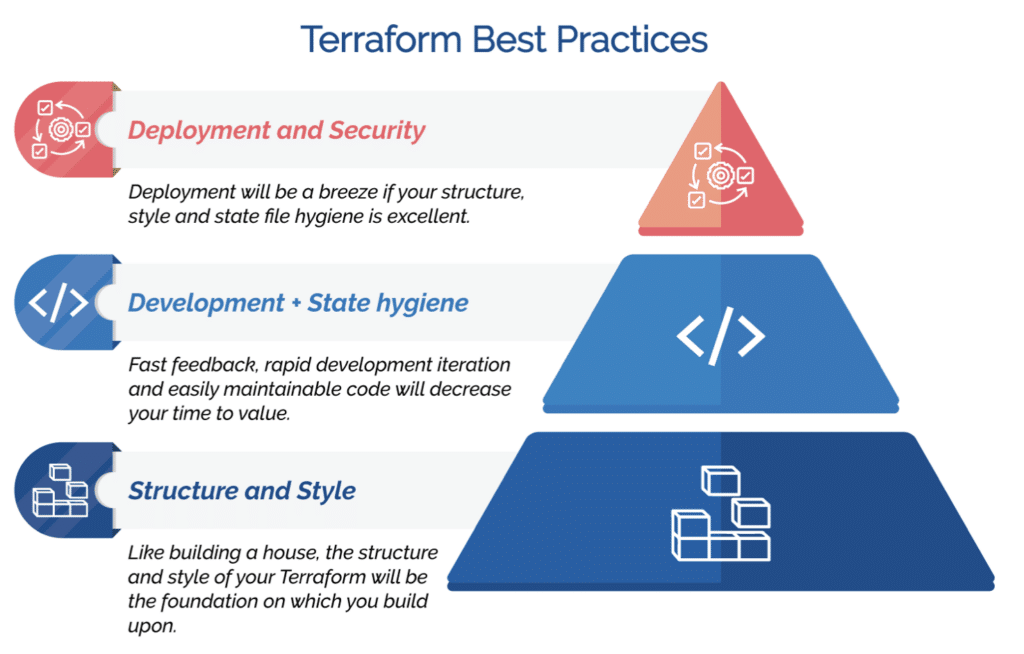
Store state in S3 with DynamoDB locking (or an Azure blob) so teams do not clobber each other. Never commit state to Git.
Modules and structure
Wrap reusable pieces in modules and separate environments so changes stay isolated and reviewable.
module "network" {
  source = "./modules/network"
  cidr   = var.vpc_cidr
}
Plan, review, apply
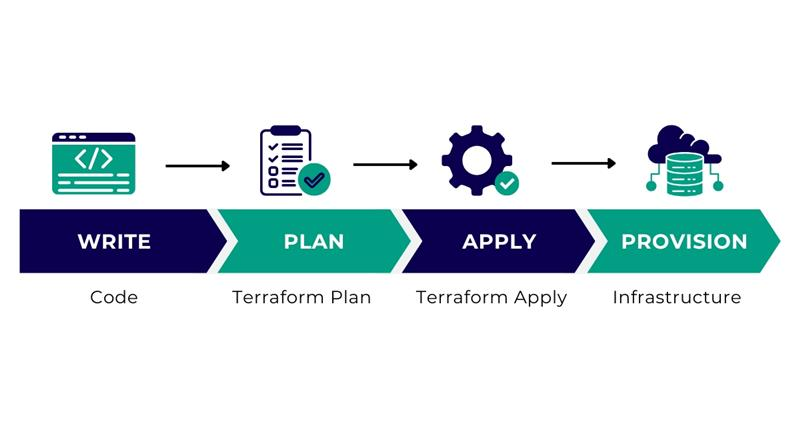
Run terraform plan in CI on every PR so changes are reviewed before apply. Pin provider versions for reproducibility.
Key Takeaways
- Keep state remote and locked to enable safe team collaboration.
- Modules make infrastructure reusable, testable and consistent.
- Run plan in CI and require review before any apply.
- Pin provider and module versions for reproducible builds.
- Never hardcode secrets — source them from Vault or a secrets manager.
Wrapping Up
Treat infrastructure like application code — modular, reviewed and versioned — and your cloud stays reproducible instead of a snowflake.
3 Comments +12
Rahul Sharma
13 May 2026Remote locked state ended our “who applied what” chaos. Essential for teams.
Diksha Singh
14 May 2026Pinning provider versions saved us from a nasty surprise upgrade. Learned the hard way.
Vivek Shah
16 May 2026Plan-in-CI with required review is exactly the guardrail we needed.